Removing an old app from your computer and removing its authorization to an email account are not always the same thing. If you tried a few email utilities before choosing your current workflow, the remaining access deserves a deliberate review.
A small-business owner switches from an older calendar integration to a new service. The desktop program is uninstalled, but it may still have an active token or consent grant. Revoking blindly could also interrupt a shared scheduling process.
Try InboxCabin free for 30 days. No credit card required.
 Start Free Trial
Why this happens—and what actually needs fixing
Think of an app permission as a key that may exist separately from the installation. Provider dashboards—not the icon on your desktop—show what access an application was granted. Google explains that revoking permissions stops future access but does not automatically erase copies of data already shared.
Convenience and security must be evaluated together
Whenever a workflow handles credentials, money, confidential documents or recipient identity, assume a busy person will occasionally make a mistake. Put the safeguard at the exact point where the mistake happens: before Send, before changing payment instructions, before revoking a permission or before an account recovery becomes urgent.
A checklist is useful because it does not depend on perfect judgment during a stressful moment. But it is not a substitute for documented organizational controls. When legal duties, regulated data or corporate sign-in policies apply, ask the responsible security or compliance owner before changing the process.
What this looks like in practice
A useful separation is “remove the program,” “end the subscription,” and “revoke the permission.” Those are three actions, often performed in different places. Uninstalling may leave account permission intact; revoking permission may interrupt automation even when the program still exists. For each old tool, identify the billable subscription, any stored company information, and the provider authorization. Make a short dependency list that includes who receives generated messages or calendar invites. Only after testing the replacement should you revoke the old permission. This avoids an embarrassing situation where a well-intentioned cleanup silently stops appointment confirmations or a necessary audit export.
Step-by-step: a process you can actually use
1. Find the provider identity
Confirm whether the connected account is personal Google, business Google Workspace, Outlook.com or employer-managed Microsoft 365.
2. Identify the app precisely
Match publisher, date, permissions and product name; avoid removing similarly named business integrations.
3. Check dependencies
Ask whether automations, calendar bookings or backups still rely on the connection.
4. Export records when appropriate
If the service stores business records, preserve them under company policy before revoking access.
5. Revoke through the official dashboard
Use Google’s connected-app controls or Microsoft’s permitted app-management workflow.
6. Test critical functions
Verify login, scheduling and notifications still work. Record which app was removed and why.
A worked example from a normal business day
The owner checks the old scheduling app, discovers that it was unused for six months, exports prior booking records, and removes consent. A newer appointment system remains untouched. The result is a smaller access footprint without disrupting active operations.
Three mistakes to avoid
- Uninstalling an app and assuming its provider consent was automatically revoked.
- Revoking shared-company permissions without notifying the owner of the integration.
- Trying to bypass the administrator for a Microsoft-managed organizational grant.
How to tell whether the change is working
Maintain a simple permission register: application, publisher, account, scope, business owner, review date, decision. Revisit it quarterly or after replacing an app.
Security and policy boundaries
A security review is not a license to access colleagues’ accounts. Administrators should use authorized controls, and employers should manage tenant-wide app consent centrally.
Where a dedicated email workspace fits
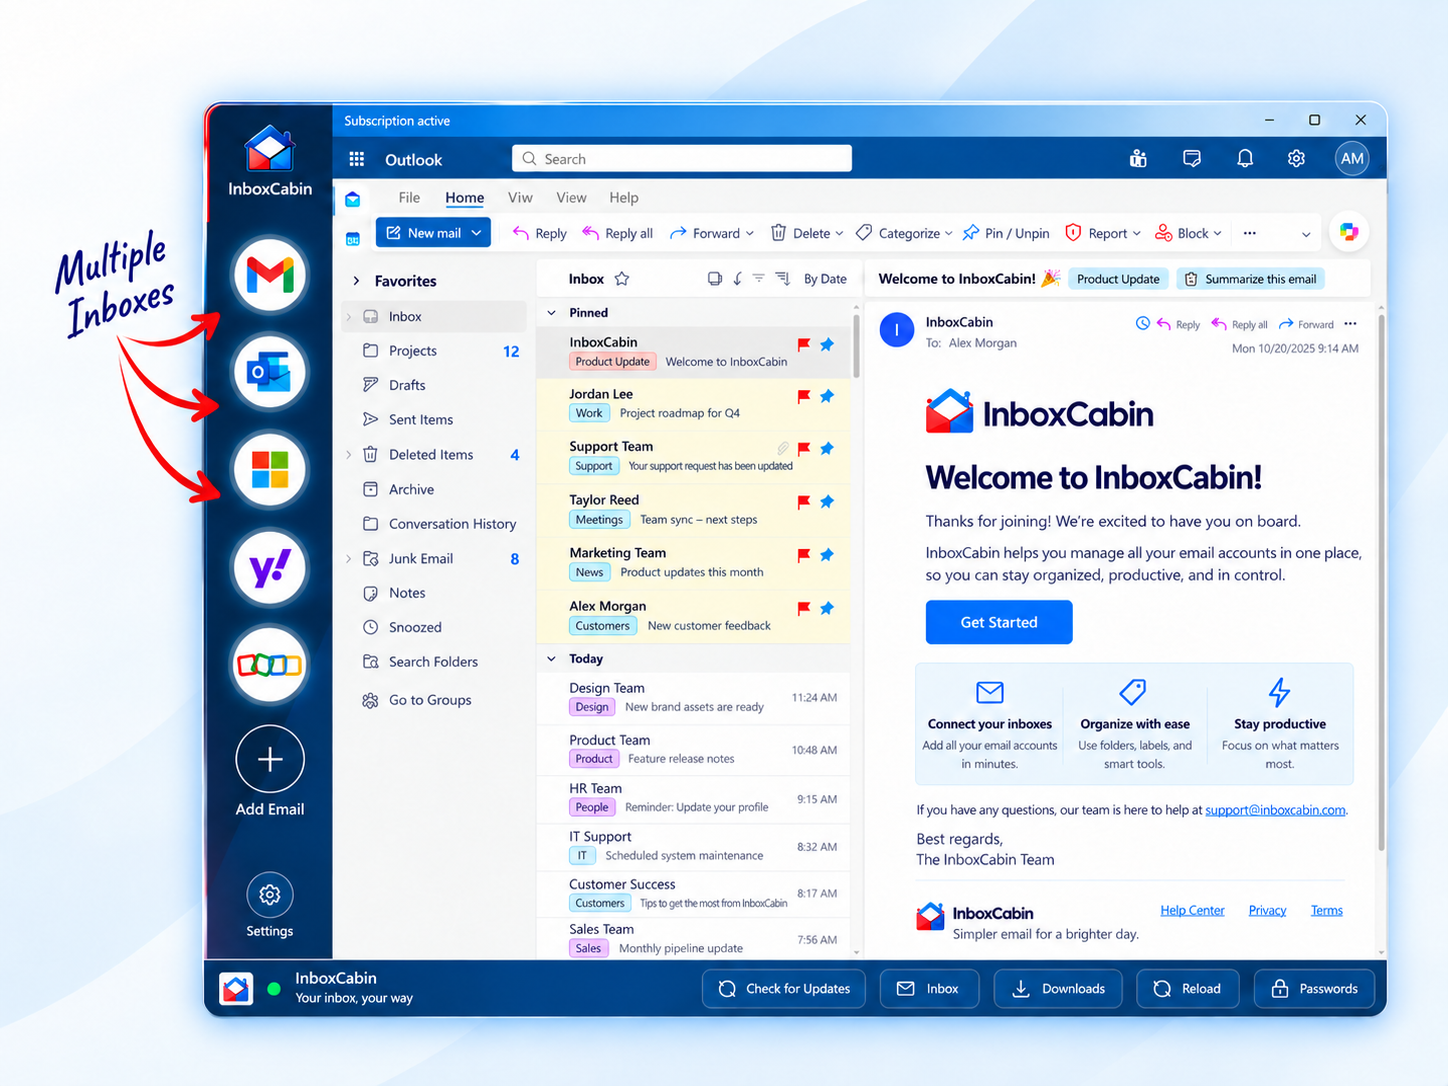
This process is separate from InboxCabin. InboxCabin may organize sign-in sessions, but provider permission removal must be done in the Google or Microsoft account settings.
Frequently asked questions
Does uninstalling an email app remove all authorization?
Not necessarily. Check the provider’s linked-app permissions separately.
Will revoking permission stop the third party from using old data?
Future access is revoked, but previously obtained copies may require a separate deletion request.
Further reading
For current provider behavior and supported controls, see Google: manage third-party access Microsoft: edit or revoke app permissions. Product interfaces change, so confirm instructions in the version your organization uses.
New to the product? Read Meet InboxCabin to see the dedicated multi-inbox workspace and how it is different from a unified mail client.
Related guides
- How to Audit Apps Connected to Your Gmail or Microsoft Account
- Locked Out of One Email Account? Build a Recovery Map Now
Explore InboxCabin for a dedicated Windows workspace that keeps Gmail and Microsoft accounts separate and easy to reach.
The takeaway
Confirm whether the connected account is personal Google, business Google Workspace, Outlook.com or employer-managed Microsoft 365.
Try InboxCabin free for 30 days. No credit card required.
Examples in this article are illustrative, not customer case studies or promises of results.