The email tool you stopped using last year may still have permission to access parts of your account. A regular connected-app audit is one of the least dramatic—and most valuable—security habits for people who use several Gmail and Microsoft identities.
A consultant experiments with scheduling tools, project extensions, newsletter services and contact utilities. Months later, some still appear in Google’s third-party connections or the Microsoft organization’s application list. Not every connection is dangerous, but the consultant no longer remembers why each exists.
Try InboxCabin free for 30 days. No credit card required.
 Start Free Trial
Why this happens—and what actually needs fixing
Separate two questions: is this application legitimate, and does it still need its current permission? Google lets users review authorized linked apps. Microsoft work-school accounts may have both user-consented and administrator-consented access, with different revocation rights.
Start with the existing provider tools and the permissions you already have. Only introduce another step when it makes the task safer, faster or more dependable.
Convenience and security must be evaluated together
Whenever a workflow handles credentials, money, confidential documents or recipient identity, assume a busy person will occasionally make a mistake. Put the safeguard at the exact point where the mistake happens: before Send, before changing payment instructions, before revoking a permission or before an account recovery becomes urgent.
A checklist is useful because it does not depend on perfect judgment during a stressful moment. But it is not a substitute for documented organizational controls. When legal duties, regulated data or corporate sign-in policies apply, ask the responsible security or compliance owner before changing the process.
What this looks like in practice
Prioritize by permission scope rather than by how unfamiliar the logo looks. An app with permission to see a basic profile has a very different risk profile from one permitted to read or modify mail. Apps used for company-wide workflows also deserve an accountable owner, even if they are trusted. Write down which business function would fail if access disappeared. If nobody knows the answer, that is a reason to investigate rather than immediately delete the grant. A good audit produces three decisions: keep with a named owner, revoke after dependency testing, or escalate to IT for administrator review. It should never require logging into someone else’s account without authorization.
Step-by-step: a process you can actually use
1. Inventory accounts
Write down every Gmail, Google Workspace, Outlook.com and Microsoft 365 identity you personally manage.
2. Open official permission pages
Use Google Account third-party connections or Microsoft’s My Apps portal rather than third-party permission scanners.
3. Read the scope
Distinguish basic profile access from reading, creating or modifying email, contacts or calendar data.
4. Ask whether the connection is still necessary
Review purpose, owner, last usage and whether another tool replaced it.
5. Revoke cautiously
Remove access you no longer need, knowing that the dependent service may stop working.
6. Document organizational exceptions
For work accounts, ask IT to review administrator-consented applications you cannot remove yourself.
A worked example from a normal business day
During a quarterly audit the consultant finds an abandoned automation service with access to mail metadata. They confirm no current workflow depends on it, revoke its permission through the provider, and note the action in their security checklist. Their calendar scheduling tool remains because the business actively uses it.
Three mistakes to avoid
- Assuming clicking Sign in with Google grants the same rights as Gmail-content access.
- Removing a business-critical connection without checking active automation.
- Assuming a user can revoke permissions granted by a Microsoft tenant administrator.
How to tell whether the change is working
Count unknown or unnecessary grants by account, record their scope and set a 90-day review reminder. Fewer unnecessary grants is more meaningful than simply having fewer apps.
Security and policy boundaries
Follow company policy and never ask employees to reveal passwords to perform the audit. Revoke permissions from the official provider, not by deleting random files or browser data.
Where a dedicated email workspace fits
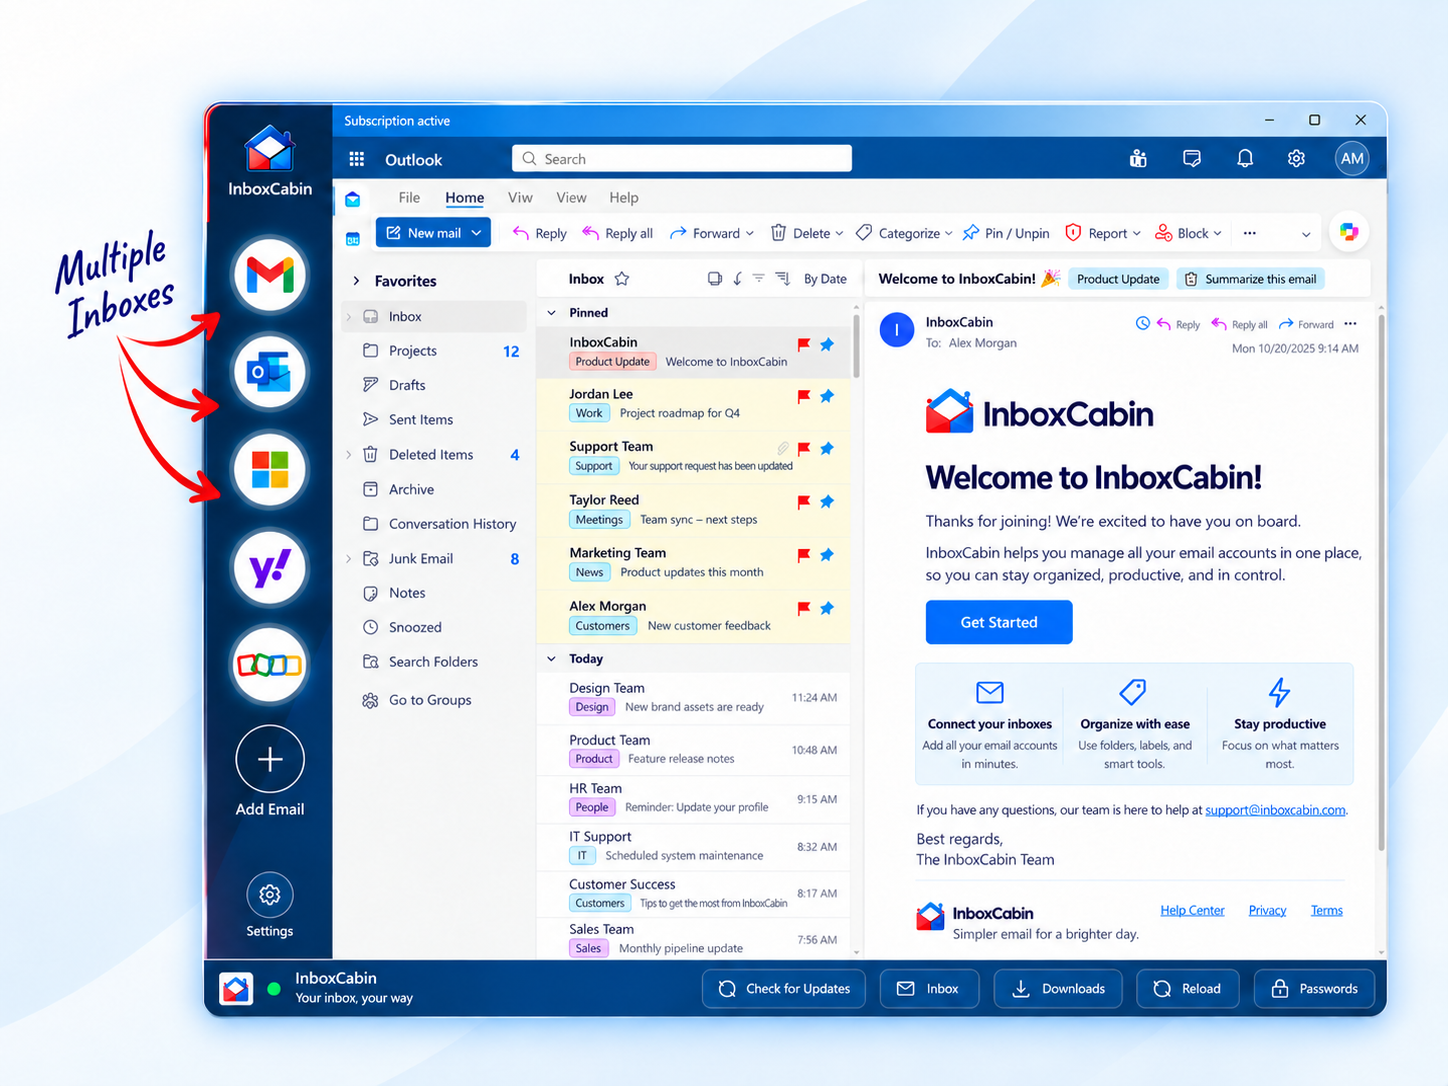
InboxCabin is an account workspace, not an app-permission auditor. Use the providers’ security dashboards for access reviews, then return to the proper account through your normal desktop workflow.
Frequently asked questions
Does removing a linked app delete its old copies of data?
Not necessarily. Google cautions that previously shared data may remain with the third party.
Can I remove administrator-approved Microsoft apps myself?
Typically not; your organization’s administrator controls those grants.
Further reading
For current provider behavior and supported controls, see Google: manage third-party access Microsoft: edit or revoke app permissions. Product interfaces change, so confirm instructions in the version your organization uses.
New to the product? Read Meet InboxCabin to see the dedicated multi-inbox workspace and how it is different from a unified mail client.
Related guides
- How to Revoke Old Email App Permissions Without Breaking Your Workflow
- Passkeys, Security Keys and MFA When You Manage Several Inboxes
Explore InboxCabin for a dedicated Windows workspace that keeps Gmail and Microsoft accounts separate and easy to reach.
The takeaway
Write down every Gmail, Google Workspace, Outlook.com and Microsoft 365 identity you personally manage.
Try InboxCabin free for 30 days. No credit card required.
Examples in this article are illustrative, not customer case studies or promises of results.