The time to learn how your email accounts recover is before your phone breaks or an employer disables your login. When you manage several identities, a simple private recovery map can turn a crisis into a process.
A solo founder uses one personal Gmail, one Microsoft 365 business account, a billing mailbox and a shared support identity. Their authenticator phone is lost during travel. They still know some passwords, but cannot complete the second-factor challenge.
Try InboxCabin free for 30 days. No credit card required.
 Start Free Trial
Why this happens—and what actually needs fixing
Account recovery is controlled by Google, Microsoft or the organization administering a work tenant—not by whichever desktop email workspace displays the account. Recovery email, security keys, backup codes and administrators may differ by identity.
The practical objective is not to add more software. It is to make a short series of decisions repeatable, so that the next employee or future you can do the work without reinventing it.
Convenience and security must be evaluated together
Whenever a workflow handles credentials, money, confidential documents or recipient identity, assume a busy person will occasionally make a mistake. Put the safeguard at the exact point where the mistake happens: before Send, before changing payment instructions, before revoking a permission or before an account recovery becomes urgent.
A checklist is useful because it does not depend on perfect judgment during a stressful moment. But it is not a substitute for documented organizational controls. When legal duties, regulated data or corporate sign-in policies apply, ask the responsible security or compliance owner before changing the process.
What this looks like in practice
Recovery plans fail when the only copy of the plan is trapped in the unavailable account. Store recovery information through an approved password manager or secure offline process and distinguish where a secret is kept from the secret itself. For a business account, record an administrator and alternate authorized contact; for a personal account, verify provider recovery methods periodically. If someone leaves the company, review ownership of support and billing inboxes before access disappears. The strongest test is a tabletop exercise: “My phone is gone and the primary admin is unreachable—what happens now?” Do not risk locking yourself out during a test; use supported recovery checks and a spare device where appropriate.
Step-by-step: a process you can actually use
1. Inventory every essential inbox
For each account record provider, purpose, owner and whether it is personal or company-managed.
2. Document approved recovery methods
Record that a security key or recovery email exists without putting secrets into an unprotected spreadsheet.
3. Check backup factors
Verify alternate supported authentication options before you need them.
4. Identify authorized administrators
Know who can restore access for company-owned accounts and how they can be contacted out of band.
5. Test your spare-device process
Perform an approved sign-in test on a backup device; do not deliberately disable security protections.
6. Store the map securely
Keep recovery references in an approved password manager or company emergency records location.
A worked example from a normal business day
The founder creates a password-manager note listing each account’s provider, responsible administrator and where the sealed backup key is stored. When the phone fails, they use the documented approved path rather than trying random passwords or contacting the wrong support team.
Three mistakes to avoid
- Storing MFA recovery codes in the very inbox they are meant to recover.
- Letting one ex-employee control every recovery method.
- Assuming a software license key can restore a Gmail or Microsoft identity.
How to tell whether the change is working
Track essential accounts with a known recovery owner and at least one tested approved backup method. Review after personnel, device or phone-number changes.
Security and policy boundaries
Do not share recovery codes with vendors or support chat agents. Follow official provider recovery channels, and recognize that some organizations prohibit self-managed backups.
Where a dedicated email workspace fits
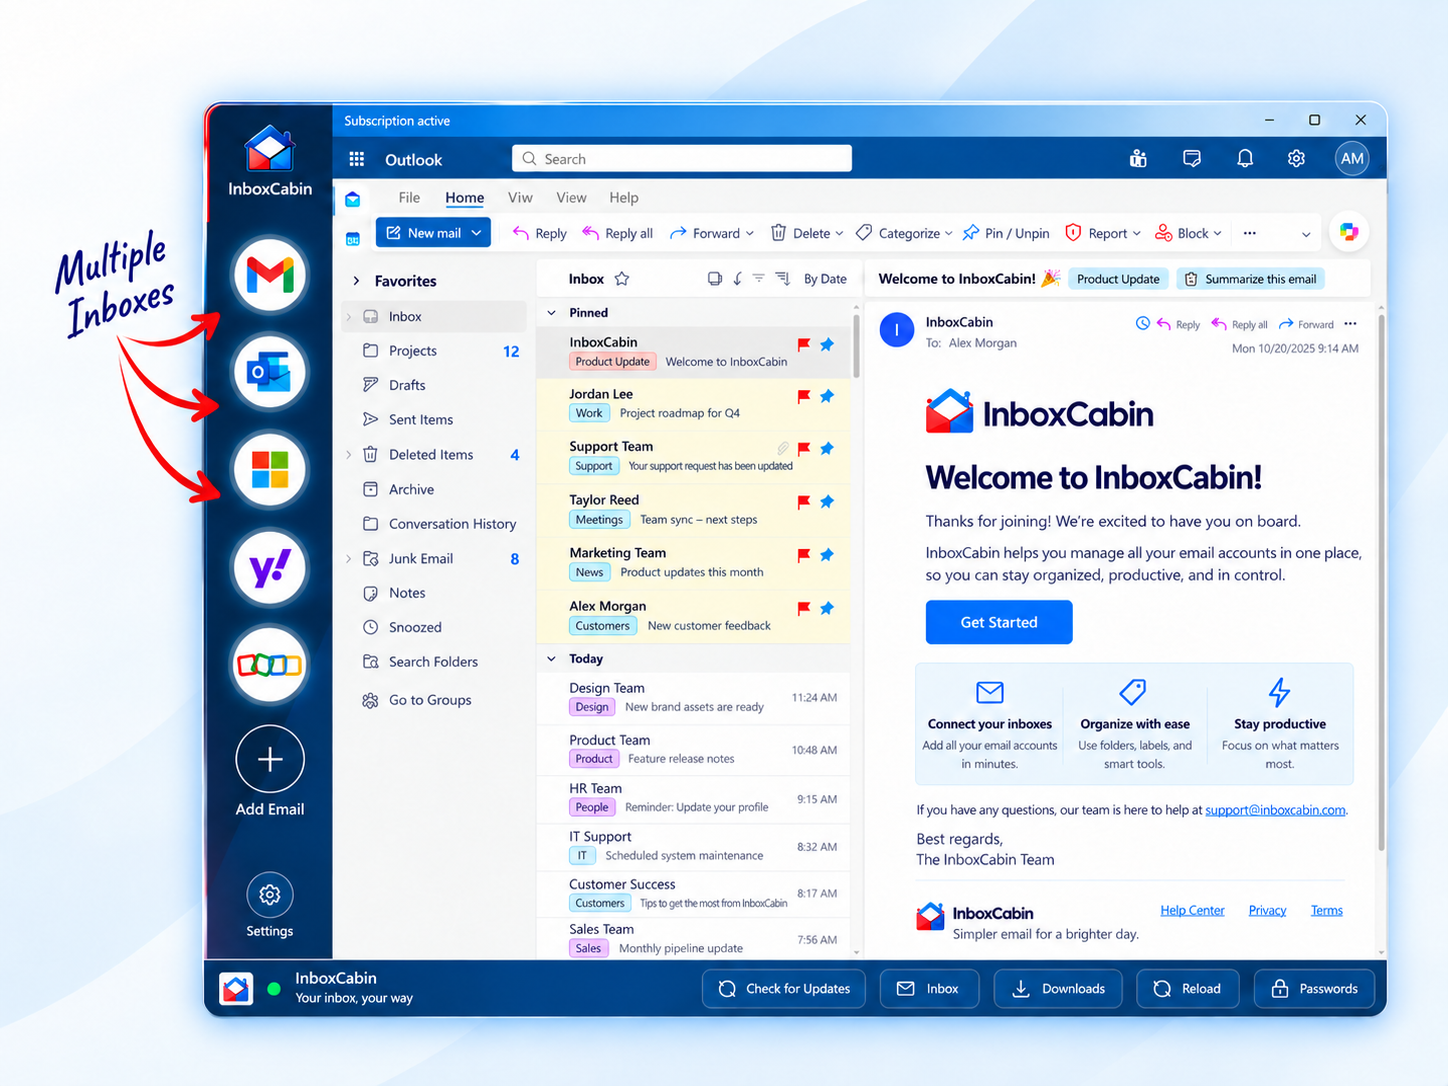
InboxCabin licensing and mailbox display do not give InboxCabin authority to reset a Google or Microsoft account. Recovery remains with the actual identity provider.
Frequently asked questions
Will reinstalling an email app fix a locked provider account?
No. You must resolve the account’s security challenge with its provider or administrator.
Should recovery codes live in ordinary email?
No. Store secrets in an appropriately protected recovery system.
Further reading
For current provider behavior and supported controls, see Google Account Security Help Microsoft Account Security Help. Product interfaces change, so confirm instructions in the version your organization uses.
New to the product? Read Meet InboxCabin to see the dedicated multi-inbox workspace and how it is different from a unified mail client.
Related guides
- Passkeys, Security Keys and MFA When You Manage Several Inboxes
- Microsoft Personal vs Work Account: Avoid Windows Sign-In Confusion
Explore InboxCabin for a dedicated Windows workspace that keeps Gmail and Microsoft accounts separate and easy to reach.
The takeaway
For each account record provider, purpose, owner and whether it is personal or company-managed.
Try InboxCabin free for 30 days. No credit card required.
Examples in this article are illustrative, not customer case studies or promises of results.