The more inboxes you manage, the more authentication prompts you encounter. That does not mean you should weaken security or try to reuse one password everywhere. It means you need a consistent identity and recovery plan for each important account.
A founder signs into personal Gmail, two Google Workspace accounts and a Microsoft 365 account on a new Windows PC. Each provider may ask for a different verification method. Without an inventory, recovery becomes a scavenger hunt of phones, keys and old backup codes.
Try InboxCabin free for 30 days. No credit card required.
 Start Free Trial
Why this happens—and what actually needs fixing
Passwordless sign-in, passkeys, physical security keys and authenticator prompts are related but not identical. Some credentials are device-bound or governed by employer rules. A desktop email workspace cannot promise to copy trusted-device status or bypass second-factor checks on a new computer.
The practical objective is not to add more software. It is to make a short series of decisions repeatable, so that the next employee or future you can do the work without reinventing it.
Convenience and security must be evaluated together
Whenever a workflow handles credentials, money, confidential documents or recipient identity, assume a busy person will occasionally make a mistake. Put the safeguard at the exact point where the mistake happens: before Send, before changing payment instructions, before revoking a permission or before an account recovery becomes urgent.
A checklist is useful because it does not depend on perfect judgment during a stressful moment. But it is not a substitute for documented organizational controls. When legal duties, regulated data or corporate sign-in policies apply, ask the responsible security or compliance owner before changing the process.
What this looks like in practice
The biggest operational risk is not MFA itself; it is a recovery plan that exists only on the phone or computer you might lose. For each critical identity, decide what happens if the primary factor disappears tonight. Personal Gmail may have recovery settings you control, while a work tenant may require your administrator. A hardware key can be a good independent backup, but only if you enroll it before the emergency and store it securely. Keep sign-in and account recovery separate from normal daily mailbox navigation. That distinction makes it easier to accept occasional provider security checks without confusing them with faults in the app displaying your inbox.
Step-by-step: a process you can actually use
1. Classify your accounts
Mark personal, business-owner and employer-controlled identities; note which ones you may administer.
2. Choose strong sign-in methods
Use provider-supported passkeys or phishing-resistant security keys where available and appropriate.
3. Enroll backups
For high-value accounts, store a second supported recovery method securely, following provider guidance.
4. Protect recovery codes
Keep them in a secure password manager or approved safe; never paste them into ordinary email drafts.
5. Test new-device login before travel
Confirm you can authenticate without the original work computer, and understand administrator approval requirements.
6. Document a loss scenario
Write down what to do if your phone fails, a security key is lost or an employee leaves.
A worked example from a normal business day
The founder configures one primary hardware key plus a backup for the most sensitive accounts, keeps authenticator recovery options current, and verifies access on a spare machine before an overseas trip. The next sign-in is not friction-free—but it is predictable and safe.
Three mistakes to avoid
- Assuming one recovery method applies automatically to every provider account.
- Saving recovery codes in an unencrypted note that syncs everywhere.
- Treating a new-computer MFA prompt as a bug to be bypassed.
How to tell whether the change is working
Count high-value accounts with two working recovery paths and test at least one recovery route per quarter. A successful tabletop test is more meaningful than the absence of MFA prompts.
Security and policy boundaries
Security options vary by Google/Microsoft account type, device and organization. Avoid promises about guaranteed portability of passkeys or login sessions.
Where a dedicated email workspace fits
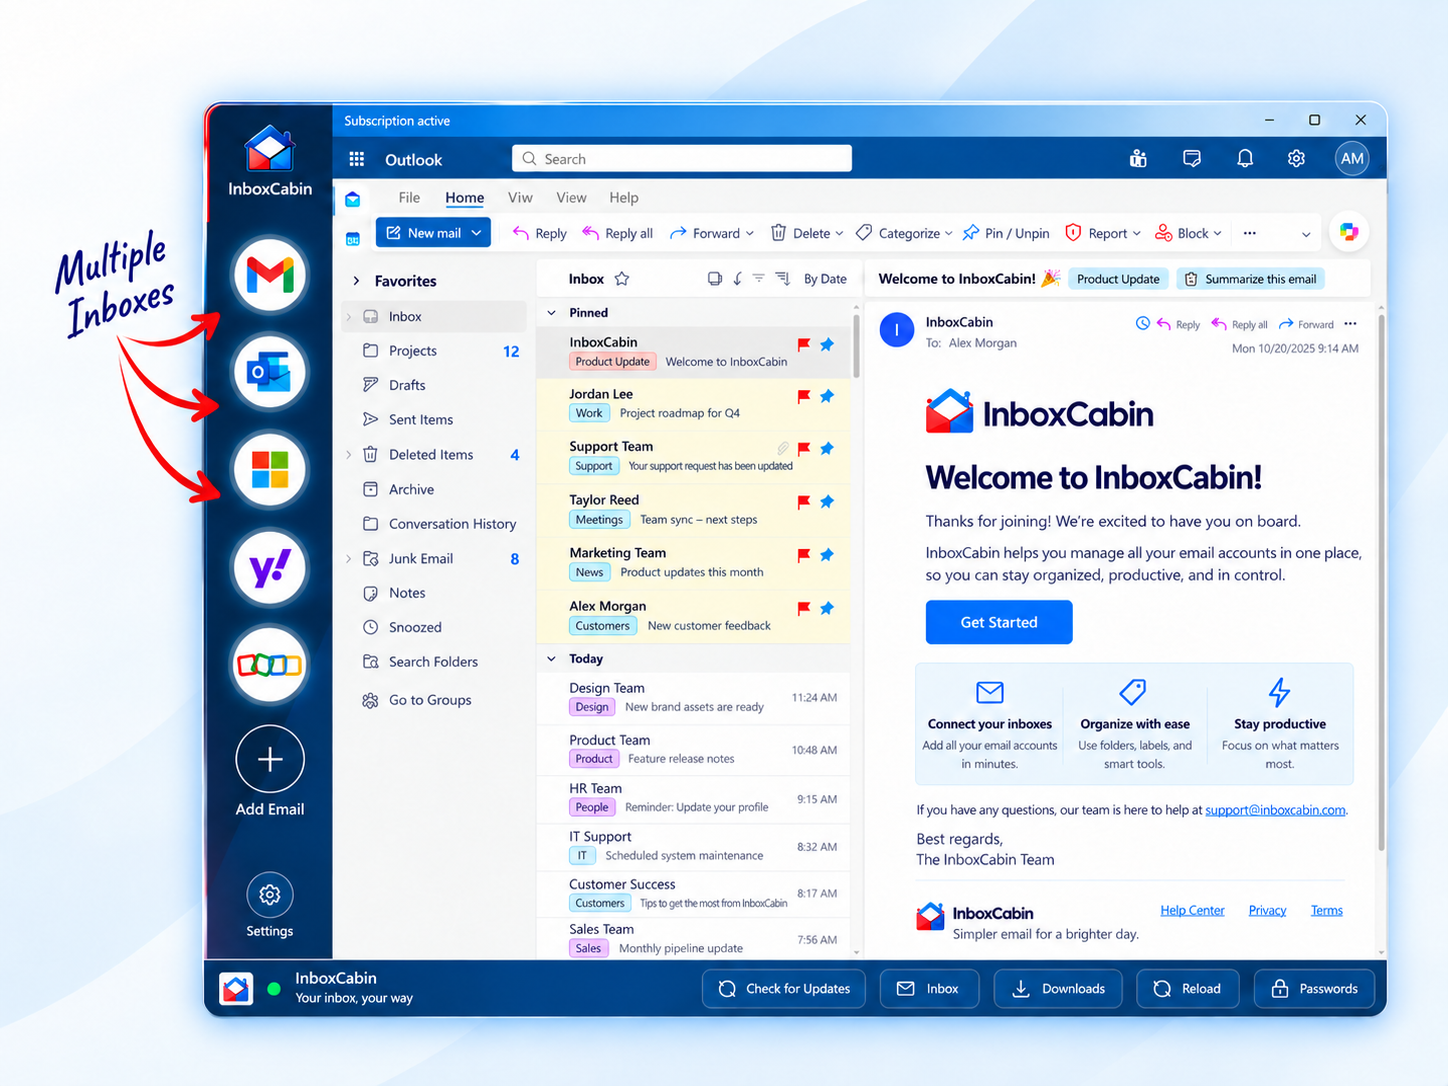
InboxCabin can hold multiple signed-in webmail sessions, but Google and Microsoft remain responsible for authenticating those accounts and enforcing MFA.
Frequently asked questions
Does moving an InboxCabin profile move an active trusted login?
Not reliably. New devices may require provider sign-in and additional verification.
Should I turn off MFA to avoid repeated prompts?
No. Diagnose the cause of repeat prompts and use approved strong authentication instead.
Further reading
For current provider behavior and supported controls, see Google: how passkeys work Microsoft Account Security Help. Product interfaces change, so confirm instructions in the version your organization uses.
New to the product? Read Meet InboxCabin to see the dedicated multi-inbox workspace and how it is different from a unified mail client.
Related guides
- How to Audit Apps Connected to Your Gmail or Microsoft Account
- Locked Out of One Email Account? Build a Recovery Map Now
Explore InboxCabin for a dedicated Windows workspace that keeps Gmail and Microsoft accounts separate and easy to reach.
The takeaway
Mark personal, business-owner and employer-controlled identities; note which ones you may administer.
Try InboxCabin free for 30 days. No credit card required.
Examples in this article are illustrative, not customer case studies or promises of results.