A small team asks whether it should share a Gmail password, make a Microsoft 365 shared mailbox, or grant employees delegated access. Those choices are not interchangeable.
The underlying question is which identity owns the messages, who may read them, and who can send under that identity.
Try InboxCabin free for 30 days. No credit card required.
 Start Free Trial
Start with the actual failure point
To locate the real cause, trace one recent message from arrival to final outcome. Where did it land? Who first saw it? Who was authorized to respond? Did the answer depend on a hidden rule or an individual remembering what to do? That walkthrough often reveals an ownership or routing issue that no new notification sound would solve.
Map the incoming messages: start with ownership
Decide whether the mail belongs to a team role such as billing@ or an individual executive account.
Name the accountable person: choose provider tools
For Microsoft 365, review shared mailbox Full Access and Send As permissions; for Gmail, review delegate access and restrictions.
Create a repeatable handoff: document access grants
Record authorized people, business justification, review date, and who revokes access after role changes.
Use a weekly exception review: test sending identity
Verify how the From field appears to recipients before staff begins using the arrangement with customers.
A realistic example: from message to resolution
Consider the original situation again: A small team asks whether it should share a Gmail password, make a Microsoft 365 shared mailbox, or grant employees delegated access. Those choices are not interchangeable. The improved version begins with a clear destination and ends with a recorded outcome. The account visible in the desktop app tells the employee where they are working; the ownership log, billing system, or approved shared-mailbox process tells them what action is authorized. Those two functions are complementary, not interchangeable.
A usable record for shared mailbox vs Gmail delegation can start as a compact shared log. Include the mailbox, accountable person, status, next action and due date; also record the factors unique to this process: choose provider tools and document access grants. Use an approved CRM, finance or case-management system once the process requires access controls, audit history or team reporting.
What not to do
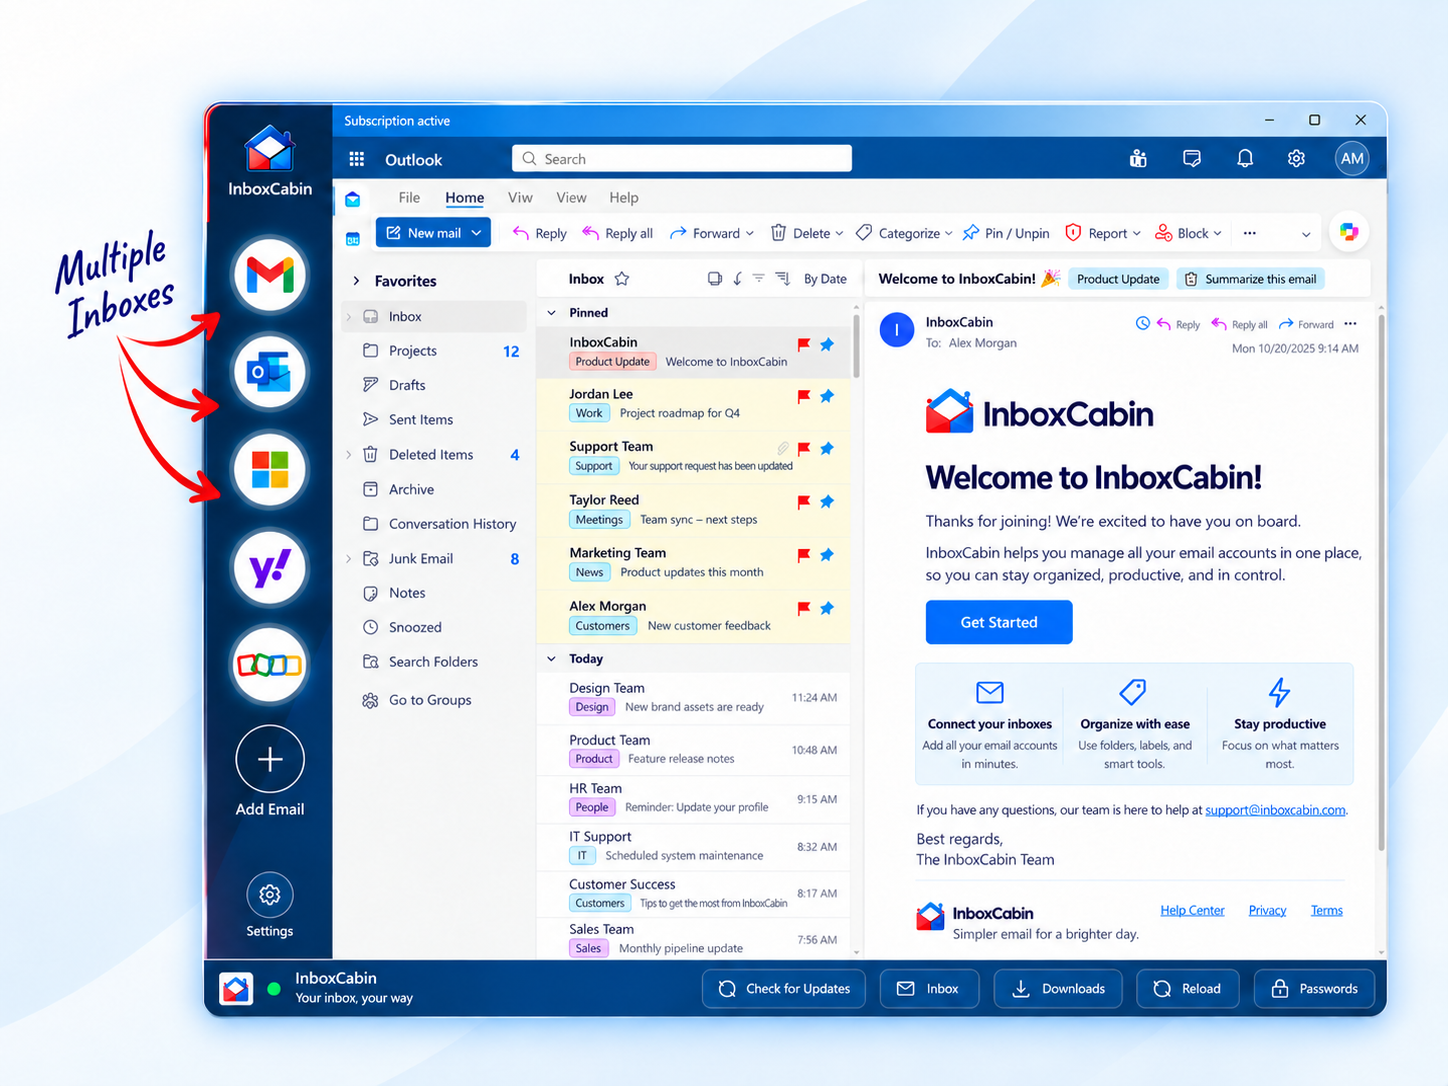
A mailbox displayed in InboxCabin does not itself grant permission to access it; provider permissions remain authoritative.
A predictable failure in this workflow is that “choose provider tools” lives only in one employee’s memory. When that person is absent, the team returns to guesswork. Prevent this by keeping instructions where the authorized backup owner can access them and by practicing the handoff before the situation becomes urgent.
How to know whether it is working
Track unauthorized access exceptions, shared passwords eliminated, and unreviewed permissions.
Where InboxCabin fits—and where it does not
InboxCabin keeps separate Gmail and Microsoft webmail accounts accessible in one Windows desktop application. It supports navigation between accounts; it does not assign conversations, approve business decisions, or grant permission to use another person’s mailbox. Keep ownership, access controls, and records in your provider and approved business systems.
For provider guidance and technical background, see this official resource. Always review current settings and policy before changing access, rules, or retention.
For related setup guidance, see managing several email accounts and avoiding replies from the wrong account.
Takeaway
The real win is not simply a cleaner-looking inbox. It is a repeatable process that turns messages into clear next actions. Start by addressing the specific failure described here: The underlying question is which identity owns the messages, who may read them, and who can send under that identity. Once responsibility, timing, and account identity are obvious, the number of inboxes becomes much less intimidating.
Try InboxCabin free for 30 days. No credit card required.
Examples in this article are illustrative, not customer case studies or promises of results.