You open a business inbox at an airport, coffee shop or hotel. The temptation is to think public Wi-Fi is either harmless or automatically catastrophic. A better approach is a short threat model: which device, which network, which credentials and which information are in play?
A consultant checks three client accounts during a layover. They also have an active laptop session, a phone hotspot and a hotel reservation email. Some messages contain invoices or employee information that would be painful to expose.
Try InboxCabin free for 30 days. No credit card required.
 Start Free Trial
Why this happens—and what actually needs fixing
Modern HTTPS protects much web traffic in transit, but public networks can still present captive portals, malicious hotspots and other risks. The greater danger may be a stolen device, weak account recovery, shoulder surfing or an unpatched operating system.
The practical objective is not to add more software. It is to make a short series of decisions repeatable, so that the next employee or future you can do the work without reinventing it.
Convenience and security must be evaluated together
Whenever a workflow handles credentials, money, confidential documents or recipient identity, assume a busy person will occasionally make a mistake. Put the safeguard at the exact point where the mistake happens: before Send, before changing payment instructions, before revoking a permission or before an account recovery becomes urgent.
A checklist is useful because it does not depend on perfect judgment during a stressful moment. But it is not a substitute for documented organizational controls. When legal duties, regulated data or corporate sign-in policies apply, ask the responsible security or compliance owner before changing the process.
What this looks like in practice
Think of the travel setup as layers rather than one magic security switch. First, know which network you actually joined. Second, use a current, locked and protected computer. Third, sign in only through recognized provider interfaces. Fourth, be realistic about physical privacy: someone over your shoulder can read a confidential email even when the connection is encrypted. Finally, follow the employer’s policy for high-risk work such as payment instructions or sensitive personal records. A trusted hotspot and a company-approved VPN may be appropriate, but neither compensates for poor recipient judgment or a stolen unlocked laptop. Test this routine before travel, not while rushing through boarding.
Step-by-step: a process you can actually use
1. Confirm the network
Ask the venue for the official Wi-Fi name and avoid lookalike networks.
2. Prefer a trusted hotspot for sensitive tasks
A mobile hotspot or approved company VPN may be preferable when policy requires it.
3. Update and lock the device
Keep Windows, browser components and security software current; use automatic lock.
4. Use MFA and trusted sign-in paths
Never enter a password into an unexpected popup or fake captive-portal copy of Outlook or Gmail.
5. Reduce shoulder surfing
Use a privacy screen where appropriate and avoid opening sensitive messages in crowded seating.
6. Sign out from borrowed machines
Better yet, avoid opening business mail on public or shared computers entirely.
A worked example from a normal business day
The consultant uses their managed laptop and approved VPN, verifies the airport network name, and handles low-risk scheduling emails. A sensitive financial approval waits until they have a private workspace and can independently verify the request.
Three mistakes to avoid
- Treating a padlock icon as proof the website or sender is legitimate.
- Signing into work mail on a kiosk or borrowed laptop.
- Leaving sensitive email content visible when the device is unattended.
How to tell whether the change is working
Audit that your device has a screen lock, current updates, working MFA and a documented travel connection policy. No list can eliminate risk, but a consistent routine reduces avoidable exposures.
Security and policy boundaries
Company policy always takes precedence; regulated data may require a managed device or restricted network. This is general risk reduction, not a guarantee of security.
Where a dedicated email workspace fits
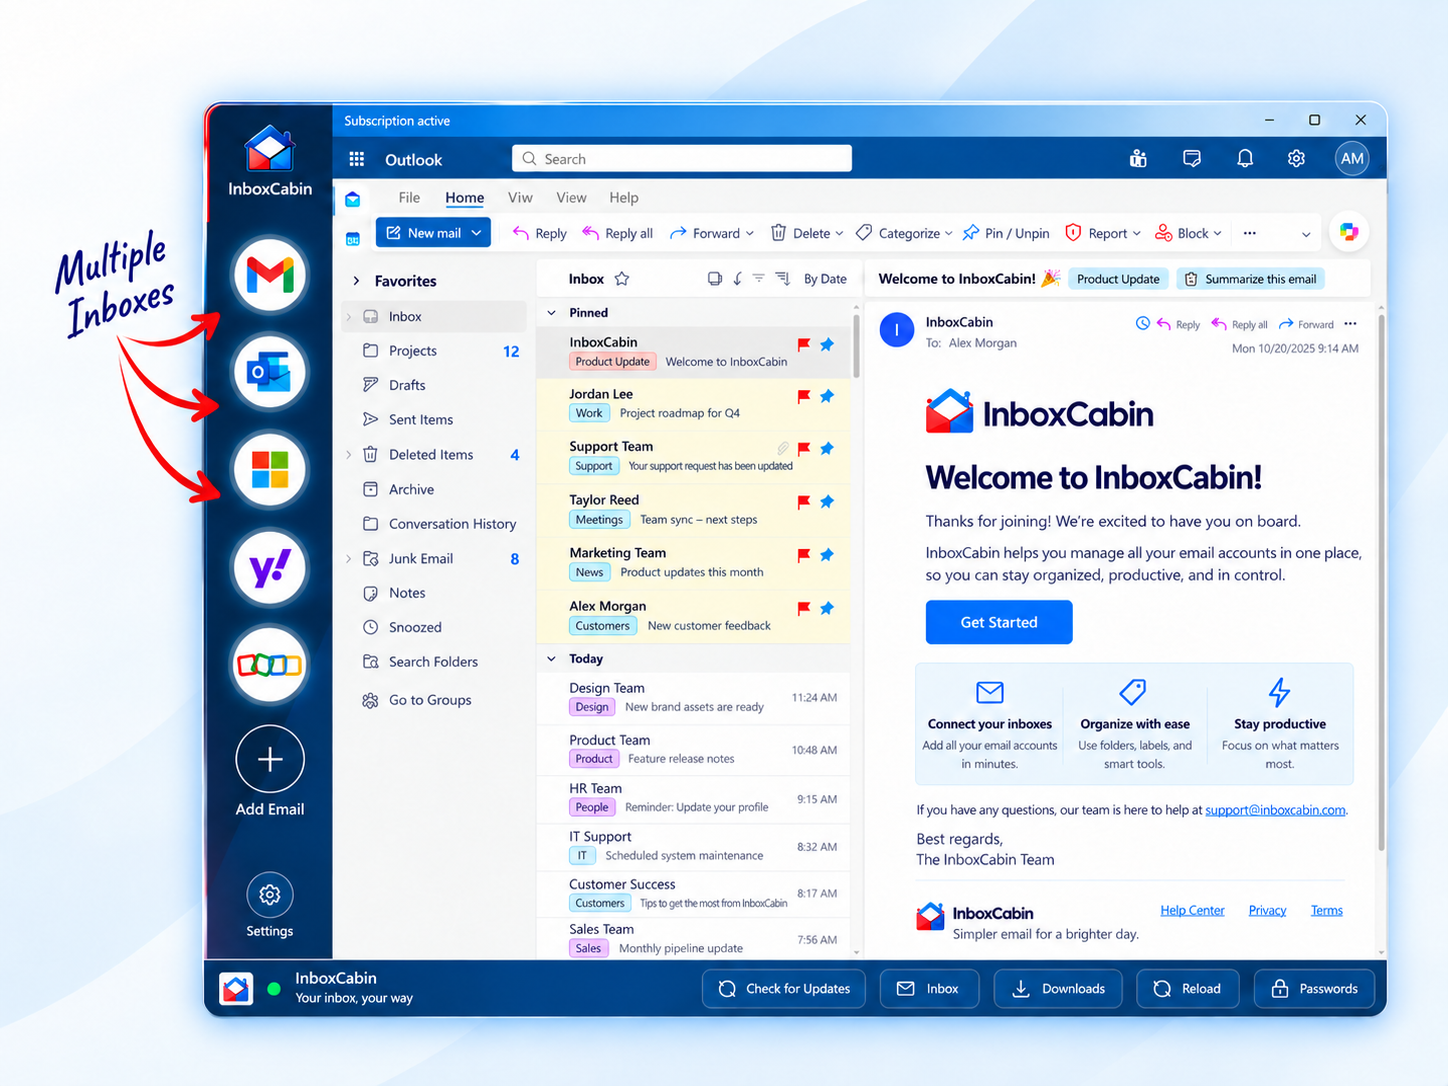
InboxCabin’s desktop workspace does not provide a VPN or protect an unsafe network. Treat it like any other app when using business email away from the office.
Frequently asked questions
Is public Wi-Fi always unsafe for Gmail or Outlook?
Risk depends on the network and device controls; avoid unknown networks and follow company policy.
Does InboxCabin encrypt public Wi-Fi traffic itself?
No special VPN or independent network-security feature is claimed.
Further reading
For current provider behavior and supported controls, see Google Account Security Help Microsoft Account Security Help. Product interfaces change, so confirm instructions in the version your organization uses.
New to the product? Read Meet InboxCabin to see the dedicated multi-inbox workspace and how it is different from a unified mail client.
Related guides
- Passkeys, Security Keys and MFA When You Manage Several Inboxes
- How to Share Email Screenshots With Support Without Leaking Private Data
Explore InboxCabin for a dedicated Windows workspace that keeps Gmail and Microsoft accounts separate and easy to reach.
The takeaway
Ask the venue for the official Wi-Fi name and avoid lookalike networks.
Try InboxCabin free for 30 days. No credit card required.
Examples in this article are illustrative, not customer case studies or promises of results.