The difficult part is not remembering several passwords. It is knowing which organization owns the current browser session, permissions and documents.
An email sent from the wrong tenant or a file opened under the wrong identity can create confusion even if no data leaves the computer. For someone with these responsibilities, keeping the right account and audience in view matters more than the number of features on an app’s pricing page.
Try InboxCabin free for 30 days. No credit card required.
 Start Free Trial
Why this issue matters in a multi-account day
A useful starting principle is tenant awareness and permission boundaries. Small changes to account identity, permission boundaries or the review schedule can matter more than replacing every tool.
A practical setup you can use this week
You do not need to rebuild your whole digital workspace to improve this. Four deliberate changes are usually easier to maintain than an impressive configuration you cannot explain six weeks later.
- Step 1. Start with the easiest change you can verify today. Identify each tenant by company name and exact sign-in address, not a vague label such as Work. If the step adds extra clicks without reducing a real source of confusion, simplify it further.
- Step 2. Treat this as an operational rule rather than a cosmetic preference. Use separate approved browser profiles or provider sessions when clients require isolation. Confirm that you can explain the result to someone else without a long walkthrough.
- Step 3. The next step is especially valuable when you work quickly. Check the organization indicator and sending identity before working with sensitive messages. Write it down in plain language so the setup is understandable after a future Windows update or a change of staff.
- Step 4. Finally, make the workflow easy to repeat on an ordinary Tuesday. Ask each customer’s IT administrator which apps and device policies are allowed. Test it with a non-sensitive test message, before deciding the configuration is complete.
An illustrative example
A fractional IT consultant helps three companies, each with its own Microsoft 365 environment. After accepting an invitation in one tenant, a link from a second client can open in the first client’s signed-in context and show an access error.
This is a fictional example, not a customer case study. Its practical takeaway is to begin with tenant awareness and permission boundaries and test that particular constraint before changing everything else. The correct configuration may differ with provider policies and company requirements.
Mistakes that make the problem worse
Most unnecessary email complexity begins with a shortcut that looks harmless. Watch out for these patterns, particularly when a second person or another business becomes involved.
- Treating guest access as equivalent to a native account in the other tenant. Convenience is appealing, but an untested shortcut can erode accountability. Make the important boundary obvious before you depend on it.
- Trying to defeat a Conditional Access policy by changing desktop wrappers. It looks efficient for a few days but leaves an invisible exception that is hard to remember later. The safer alternative is a rule that survives distraction.
- Using a shared personal browser profile for multiple regulated clients. This commonly shifts the problem to the next person or device instead of solving it. Clear ownership and validation prevent repeated cleanup work.
Where a dedicated desktop email workspace fits
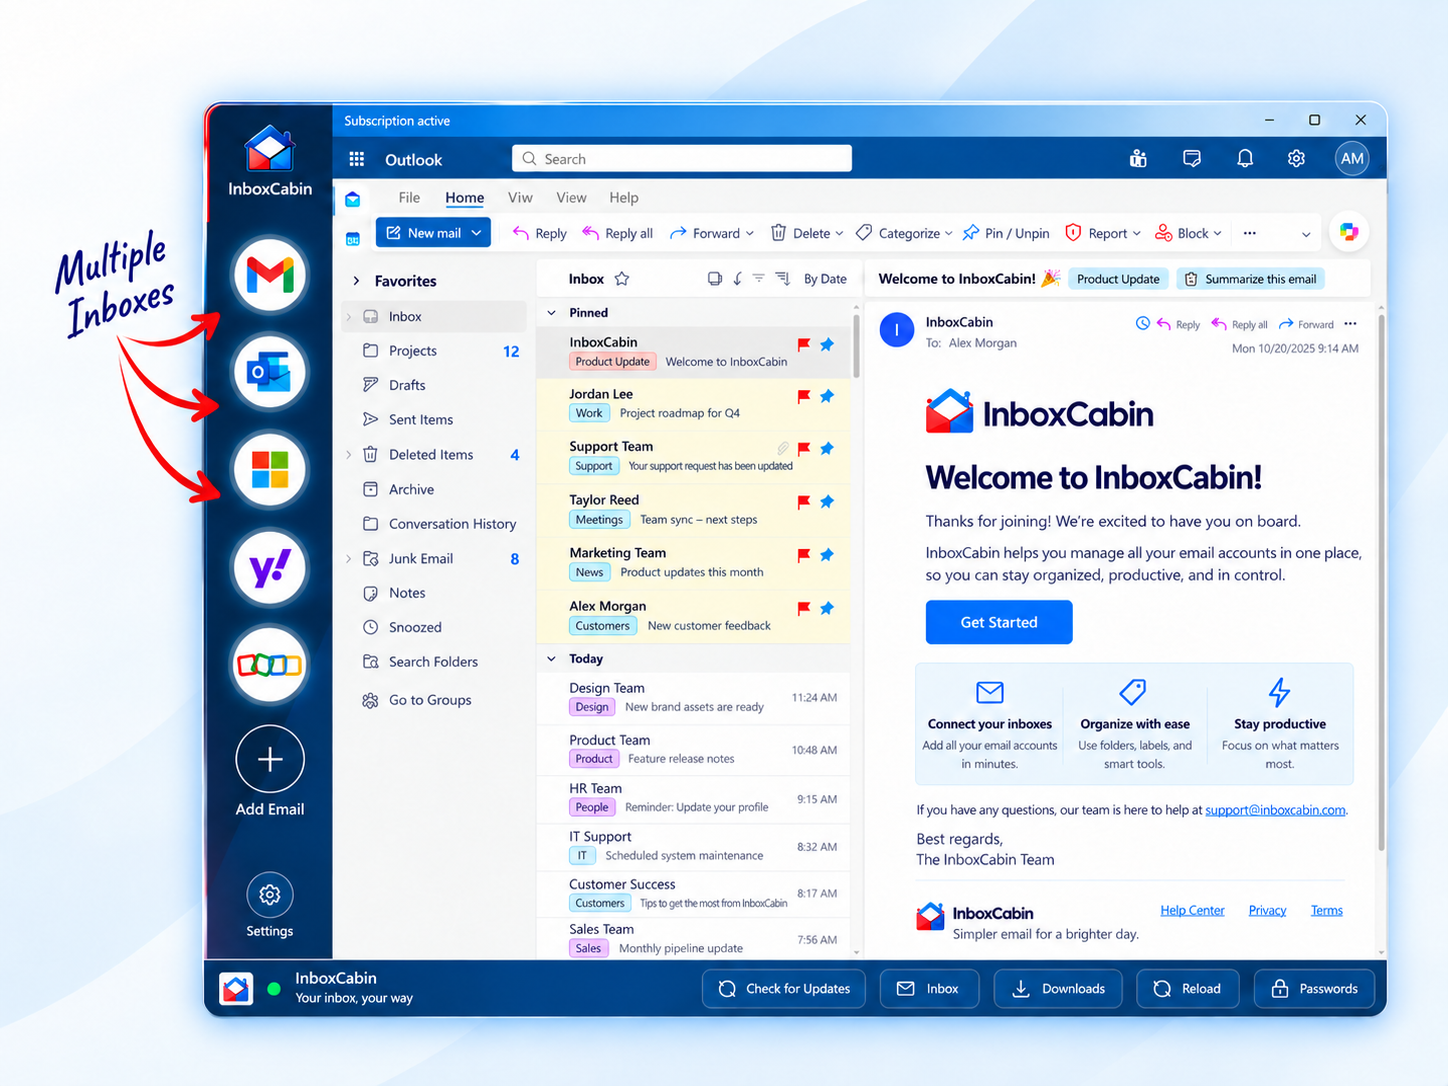
InboxCabin may organize allowed Microsoft webmail sessions, but enterprise tenant and security policies remain authoritative; some organizations will block third-party desktop containers.
Organizing who owns and uses each mailbox is one choice; choosing a convenient Windows interface for those mailboxes is another. InboxCabin may help with the latter. Keep permissions, authentication and storage decisions with the provider and your organization.
Keep the system reliable after setup
The most useful systems are not static. Accounts change, staff leave, products launch and permissions get reviewed. A short maintenance routine prevents your clean setup from quietly becoming confusing again.
- Retest access after a customer changes MFA or managed-device rules. Keep the review tied to existing work instead of turning it into another elaborate productivity ritual.
- Revoke unused guest invitations and close no-longer-required accounts. A short periodic check is often enough; the goal is preventing small assumptions from becoming permanent problems.
- Keep a clean troubleshooting log identifying tenant and policy rather than writing down passwords. If the situation has changed, update the process rather than keeping an obsolete rule out of habit.
Frequently asked questions
Where should I start?
Identify each tenant by company name and exact sign-in address, not a vague label such as Work. That is a practical starting point because it is observable and easy to verify without restructuring all your accounts.
What is a common mistake to avoid?
Treating guest access as equivalent to a native account in the other tenant. Compare the outcome against your actual daily tasks before adding another workaround.
Does InboxCabin replace Gmail or Microsoft security settings?
No. InboxCabin may organize allowed Microsoft webmail sessions, but enterprise tenant and security policies remain authoritative; some organizations will block third-party desktop containers.
Related guides
- How to Organize Multiple Google Workspace Accounts for Work
- Separate Browser Sessions: What They Protect and What They Do Not
- How to Handle MFA Prompts When Switching Between Email Accounts
Explore InboxCabin’s Windows email workspace to see how separate Gmail and Microsoft inboxes fit together.
Official resources and further reading
Provider behavior and security controls can change. These official references are useful when you need to verify a setting or limitation before acting:
The bottom line
The strongest first improvement is to focus on tenant awareness and permission boundaries. That makes the decision small enough to test without disrupting every other email account you rely on.
The place to start is practical: Identify each tenant by company name and exact sign-in address, not a vague label such as Work. Build from that baseline rather than assuming that more tabs, accounts or features will solve the problem by themselves.
Try InboxCabin free for 30 days. No credit card required.